
Cyber attack on CONPET: how oil transportation was saved
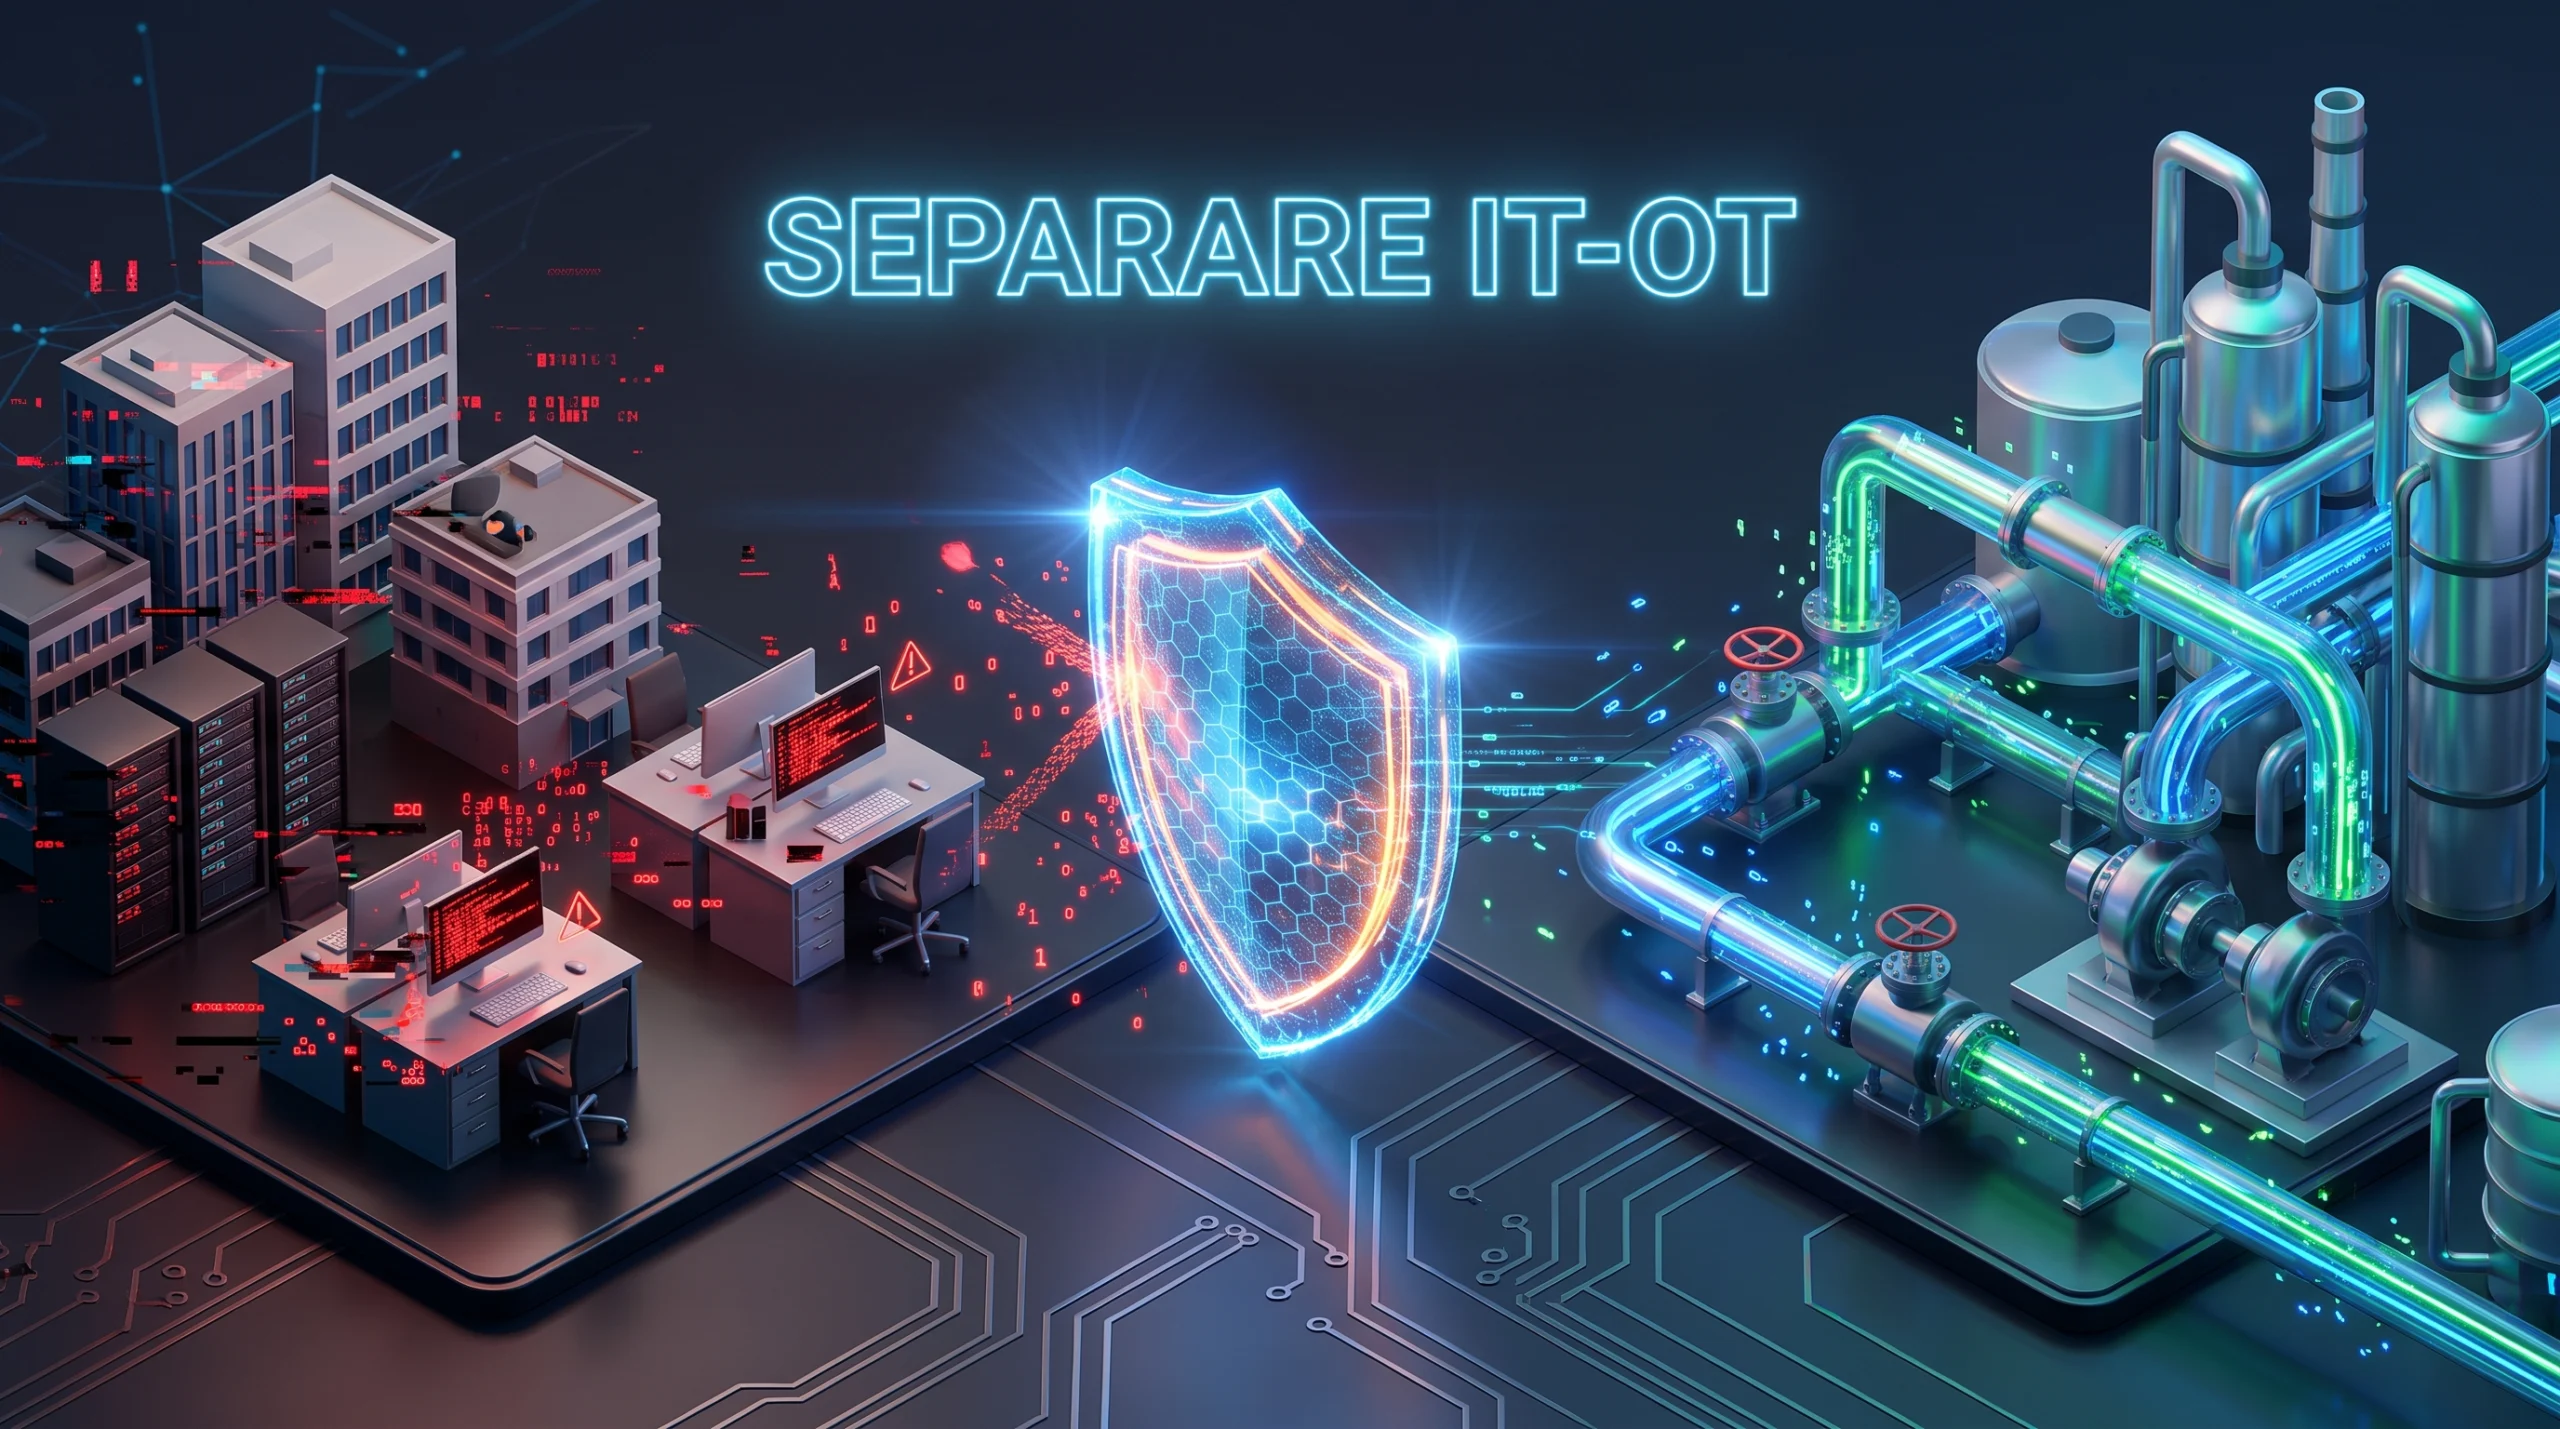
CONPET SA's business IT infrastructure was attacked by cyberattacks. The incident occurred on February 3, 2026. This company is the operator of the National Oil Transportation System. Their official website temporarily became completely inaccessible to visitors. However, the national transport of crude oil and gasoline continued normally. The official press release on February 4 immediately explained the reason for the success. The industrial control SCADA systems were not affected at all. The separation of the office network from the industrial one was essential. This intelligent separation turned the incident into a simple short news story. Avoiding a major energy crisis was a real success. Let's see how this protective barrier works in practice. Any entrepreneur with production facilities must understand this concept.
What happened during the attack at CONPET?
The company officially announced the attack on its business network. The equipment that physically controls the oil pumps remained intact. The internal telecommunications network functioned without interruption. CONPET immediately notified the prosecutors within DIOCT for an investigation. They also worked closely with cybersecurity authorities. The deep technical details of the initial attack have not been released. We will not speculate at all on this technical information. What really matters enormously is the decision that was not made. The operators were not forced to shut down the pumps at any point. If the computers had shared the same network, the shutdown would have been inevitable. It would have been a disaster similar to other recent high-profile cases.
Why is network separation a vital decision?
The office computer (IT) network is always the most exposed part. This is where we find email boxes, accounting applications and web browsers. It is where almost every modern cyber attacker enters. On the other hand, the industrial (OT) network produces a physical impact. If the industrial area is compromised, the pumps get out of control. An infected factory not only loses its website, but also stops its machinery. A technical auditor will ask one extremely simple question. If the attacker completely controls the office computers, what happens to production? The correct and healthy answer should always be „absolutely nothing”. The attacker is not allowed to move from one network to another unnoticed.
| Technical security measure | The protective effect in practice |
|---|---|
| Completely separate zones (Firewall) | The business network is physically separated from the machines in the hall. The virus is blocked at the gate. |
| Separate access accounts | The accountant's password provides absolutely no right to modify industrial orders. |
| Supplier control (MFA) | External providers connect to machines only using two-step authentication. |
Where does the chain break in smaller factories?
We often carry out technical assessments in many small industrial companies. We visit factories, water treatment plants or various local operators. Unfortunately, we very often encounter the exact opposite of the success story. We find a single flat and barrier-free computer network. The machine server is permanently on the same network as the employees' laptops. Any virus received by e-mail reaches the control line directly. Automation suppliers often log in remotely directly to the equipment. They use a simple and common password for their entire team. There is no connection history and no complex and secure authentication. In addition, backup copies of the equipment are completely missing.
What would have changed the outcome of this incident for the worse?
At CONPET, the outcome of the attack was extremely good. But how could it have ended in a real technical disaster? A single office account with access to production was fatal. A simple forgotten firewall rule opened brought immediate chaos. A direct access of the supplier offered an uncontrolled entrance to hackers. Any small breach turns a cyber attack into a transportation stop. This is exactly why the European NIS2 directive appeared. This legislation requires defense measures absolutely proportional to the great risk. Network segmentation is actually the first completely mandatory measure today. Any modern company with physical processes urgently needs it.
What can you do this very week for your factory?
Take a moment and draw out the areas of your company on paper. Check with your IT team immediately if you have a functioning firewall between them. If the network is completely open, your factory is only living on hope. List absolutely all external access routes of all partners. Make sure absolutely everyone uses only two-factor authentication. Find employees who have full access to both company networks. Start separating their accounts and their technical privileges today. Urgently ask your partners for backups of their production machines. Make a IT audit for companies with the aim of preventing disaster. Specialists can configure the latest cybersecurity solutions available today. Request support on the support page contact and let's secure the technological lines.

Leave a reply