
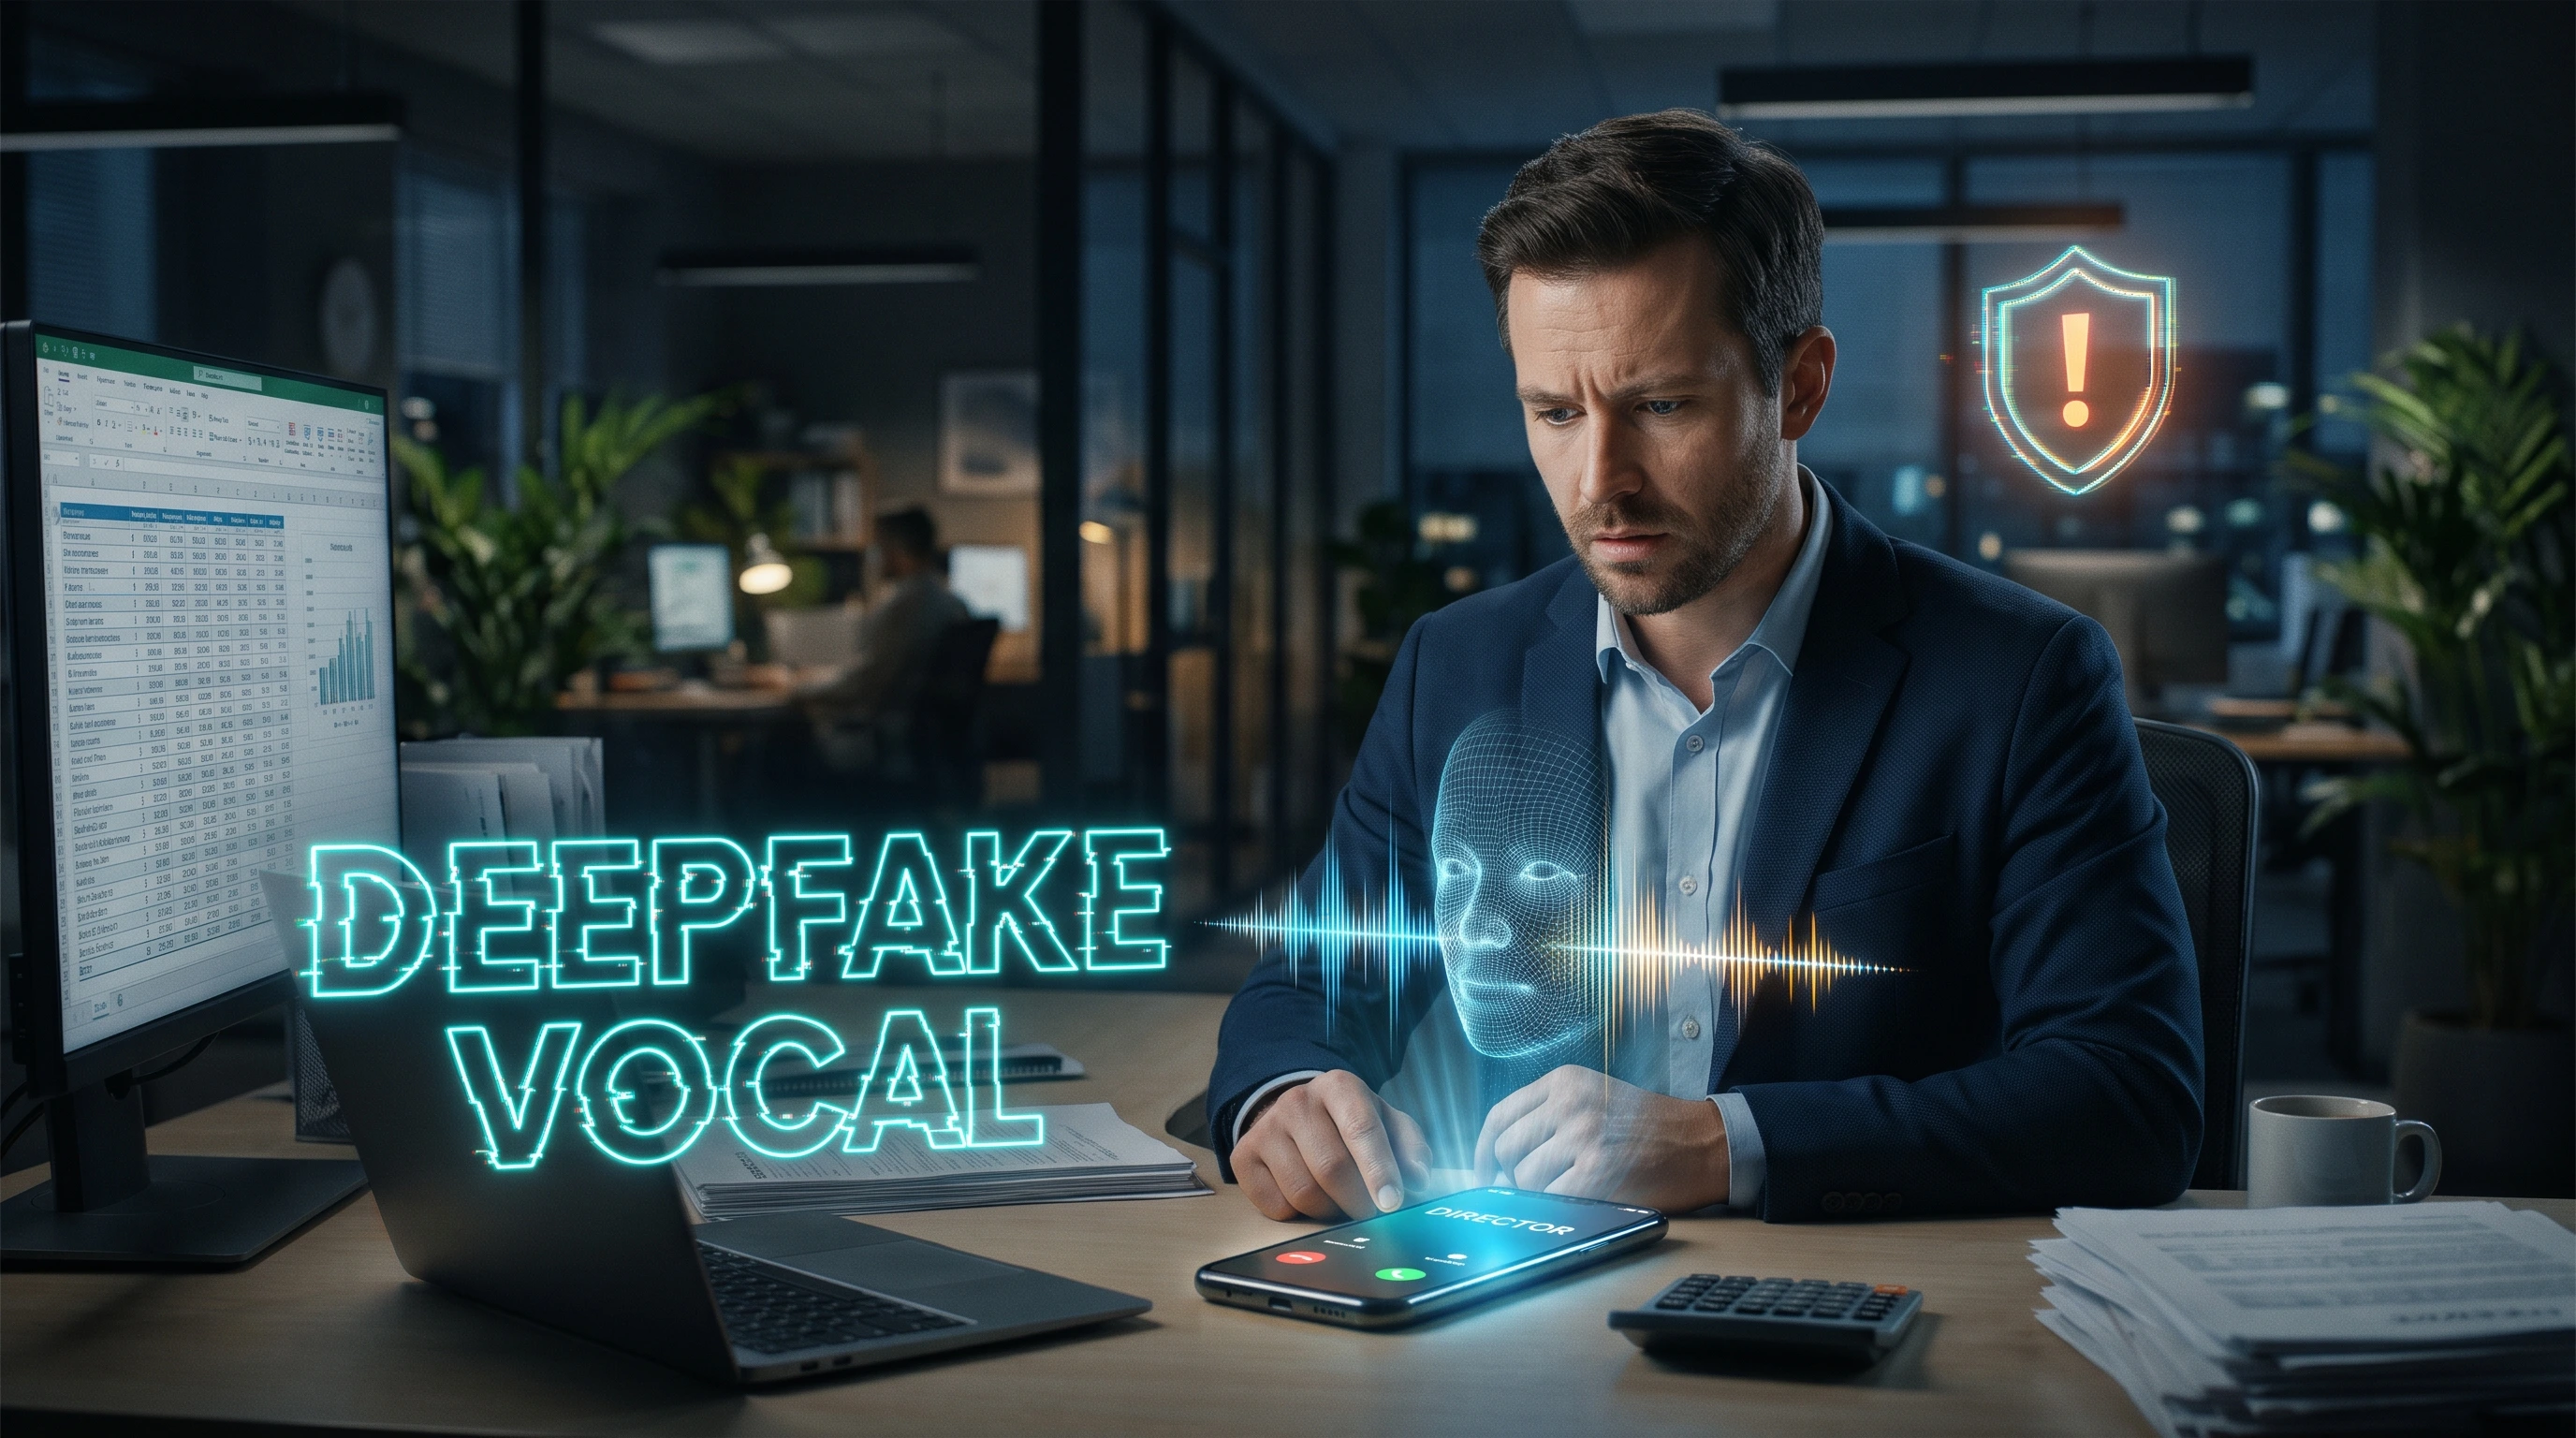
Voice deepfake and the "director's" call to accounting
Voice deepfake means a synthetic voice. It is generated by an artificial intelligence model. This mimics the tone and rhythm of a real person. Applied to fraud, it produces an extremely dangerous call. The "director" calls accounting and demands an urgent transfer. The voice sounds exactly like the director. Also, this voice deepfake represents a major threat.
A new reality for company security
As a security auditor, I treat this scenario very seriously. We must accept a shift in the basic assumption. The known voice is no longer an authentication factor. Therefore, vulnerable companies approve payments based on a flawed principle. This is: "I recognized him on the phone". That control has just expired.
The impact of phone frauds
DNSC reports from July 2026 show worrying data. 42% of frauds in the first half of the year were phone-based. Most represent classic vishing. There, a stranger pretends to be a bank. So, a voice deepfake is the logical extension. We have the same channel and the same pressure. However, now there is a trusted voice.
The attack surface: what does the attacker need for a voice deepfake?
Publicly available voice material exists for almost any manager. We easily find interviews, presentations, or short video clips. And cloning tools are accessible to anyone, without technical knowledge. Furthermore, the cost of an attack drops enormously today. When the target remains vulnerable, the attack probability massively increases.
Necessary conditions for a successful fraud
Voice material is clearly the first absolute requirement. This consists of public recordings of the targeted person. The more visible the manager, the easier it is. Also, context is vital. The attacker finds out who approves payments and who executes them. He knows exactly what projects are ongoing. This data is quickly obtained from websites or professional networks.
The ideal timing chosen by criminals
Timing is, in conclusion, crucial for a voice deepfake attack. The director must be on a publicly announced trip. Usually, everything happens at the end of the month, with a pending transaction. The call must come when you cannot personally verify it. However, a flawed payment process is the essential element. Without verbal approval, the rest yields nothing.
How the voice deepfake call unfolds
We have the example of a distribution company with 60 employees. The director is away at a trade fair abroad. On Thursday at 4:40 PM, the chief accountant receives a suspicious call. The number is unknown, and the caller says: "I'm calling from the hotel phone". Therefore, the voice is the director's. It has the same pauses and the same way of saying her name. This voice deepfake is absolutely convincing.
Key elements of psychological manipulation
He requests a quick transfer to a new supplier. It represents an advance for a strictly confidential purchase. The money must be sent before the bank closes. The invoice arrives via email in just two minutes. The address strikingly resembles a real supplier's. Also, the three elements highlighted by DNSC are present. We have emotion, urgency, and the request.
Salvation coming from pure chance
Thus, accompanied by a known voice, these do not seem like warning signs. It just seems like a typical day with a rushed boss. The payment was stopped by pure chance. The accountant called the director's wife for something completely different. Thus she found out he was actually on a plane. In conclusion, a control that works by chance is not a control.
| Protection Measure | How it works and why it is essential |
|---|---|
| 1. Second-channel verification | Any phone payment request is rigorously confirmed. The employee initiates a call to the person's known number. The cost is zero. |
| 2. Segregation of duties | The person initiating a payment does not approve it. Over a certain threshold, two approvals are required exclusively in the banking app. |
| 3. Verification question | A verification question is established between management and finance. A voice deepfake model will not know the answer. |
| 4. Urgency policy | There is a clear policy that urgency does not bypass procedure. This must be strictly signed and assumed by the director. |
What you can do quickly to prevent a voice deepfake
Decide, in writing, on a golden rule. No payment is executed based on a simple phone call. This applies regardless of the caller. The director signs this document first. Clearly establish the threshold for two approvals in the banking app. Urgently configure this rule in the system. Any voice deepfake requires strict measures.
Testing internal security procedures
Agree on a secret verification question between management and finance. This must be established only face-to-face. Additionally, schedule a useful test. Conduct a simulated call, strictly with management's agreement. Then discuss the result openly and without blame.
Evaluating the company's payment system
This voice deepfake does not introduce a new attack. It only eliminates an old and dangerous certainty. The known voice no longer proves any identity. Companies with independent payment procedures are safe. Those relying on voice recognition have an open risk. In conclusion, immediately evaluate the payment approval process.
Call experts anytime for total security
We can always bring a simple solution. This will keep the whole system in a safe place. Therefore, contact our experts by visiting the contact form on the site. You will quickly receive the appropriate IT support. We always help your businesses by conducting a complete IT audit for companies. We immediately find any vulnerabilities. In addition, we bring perfect cybersecurity solutions for your business. These are meant to fully support office work.