
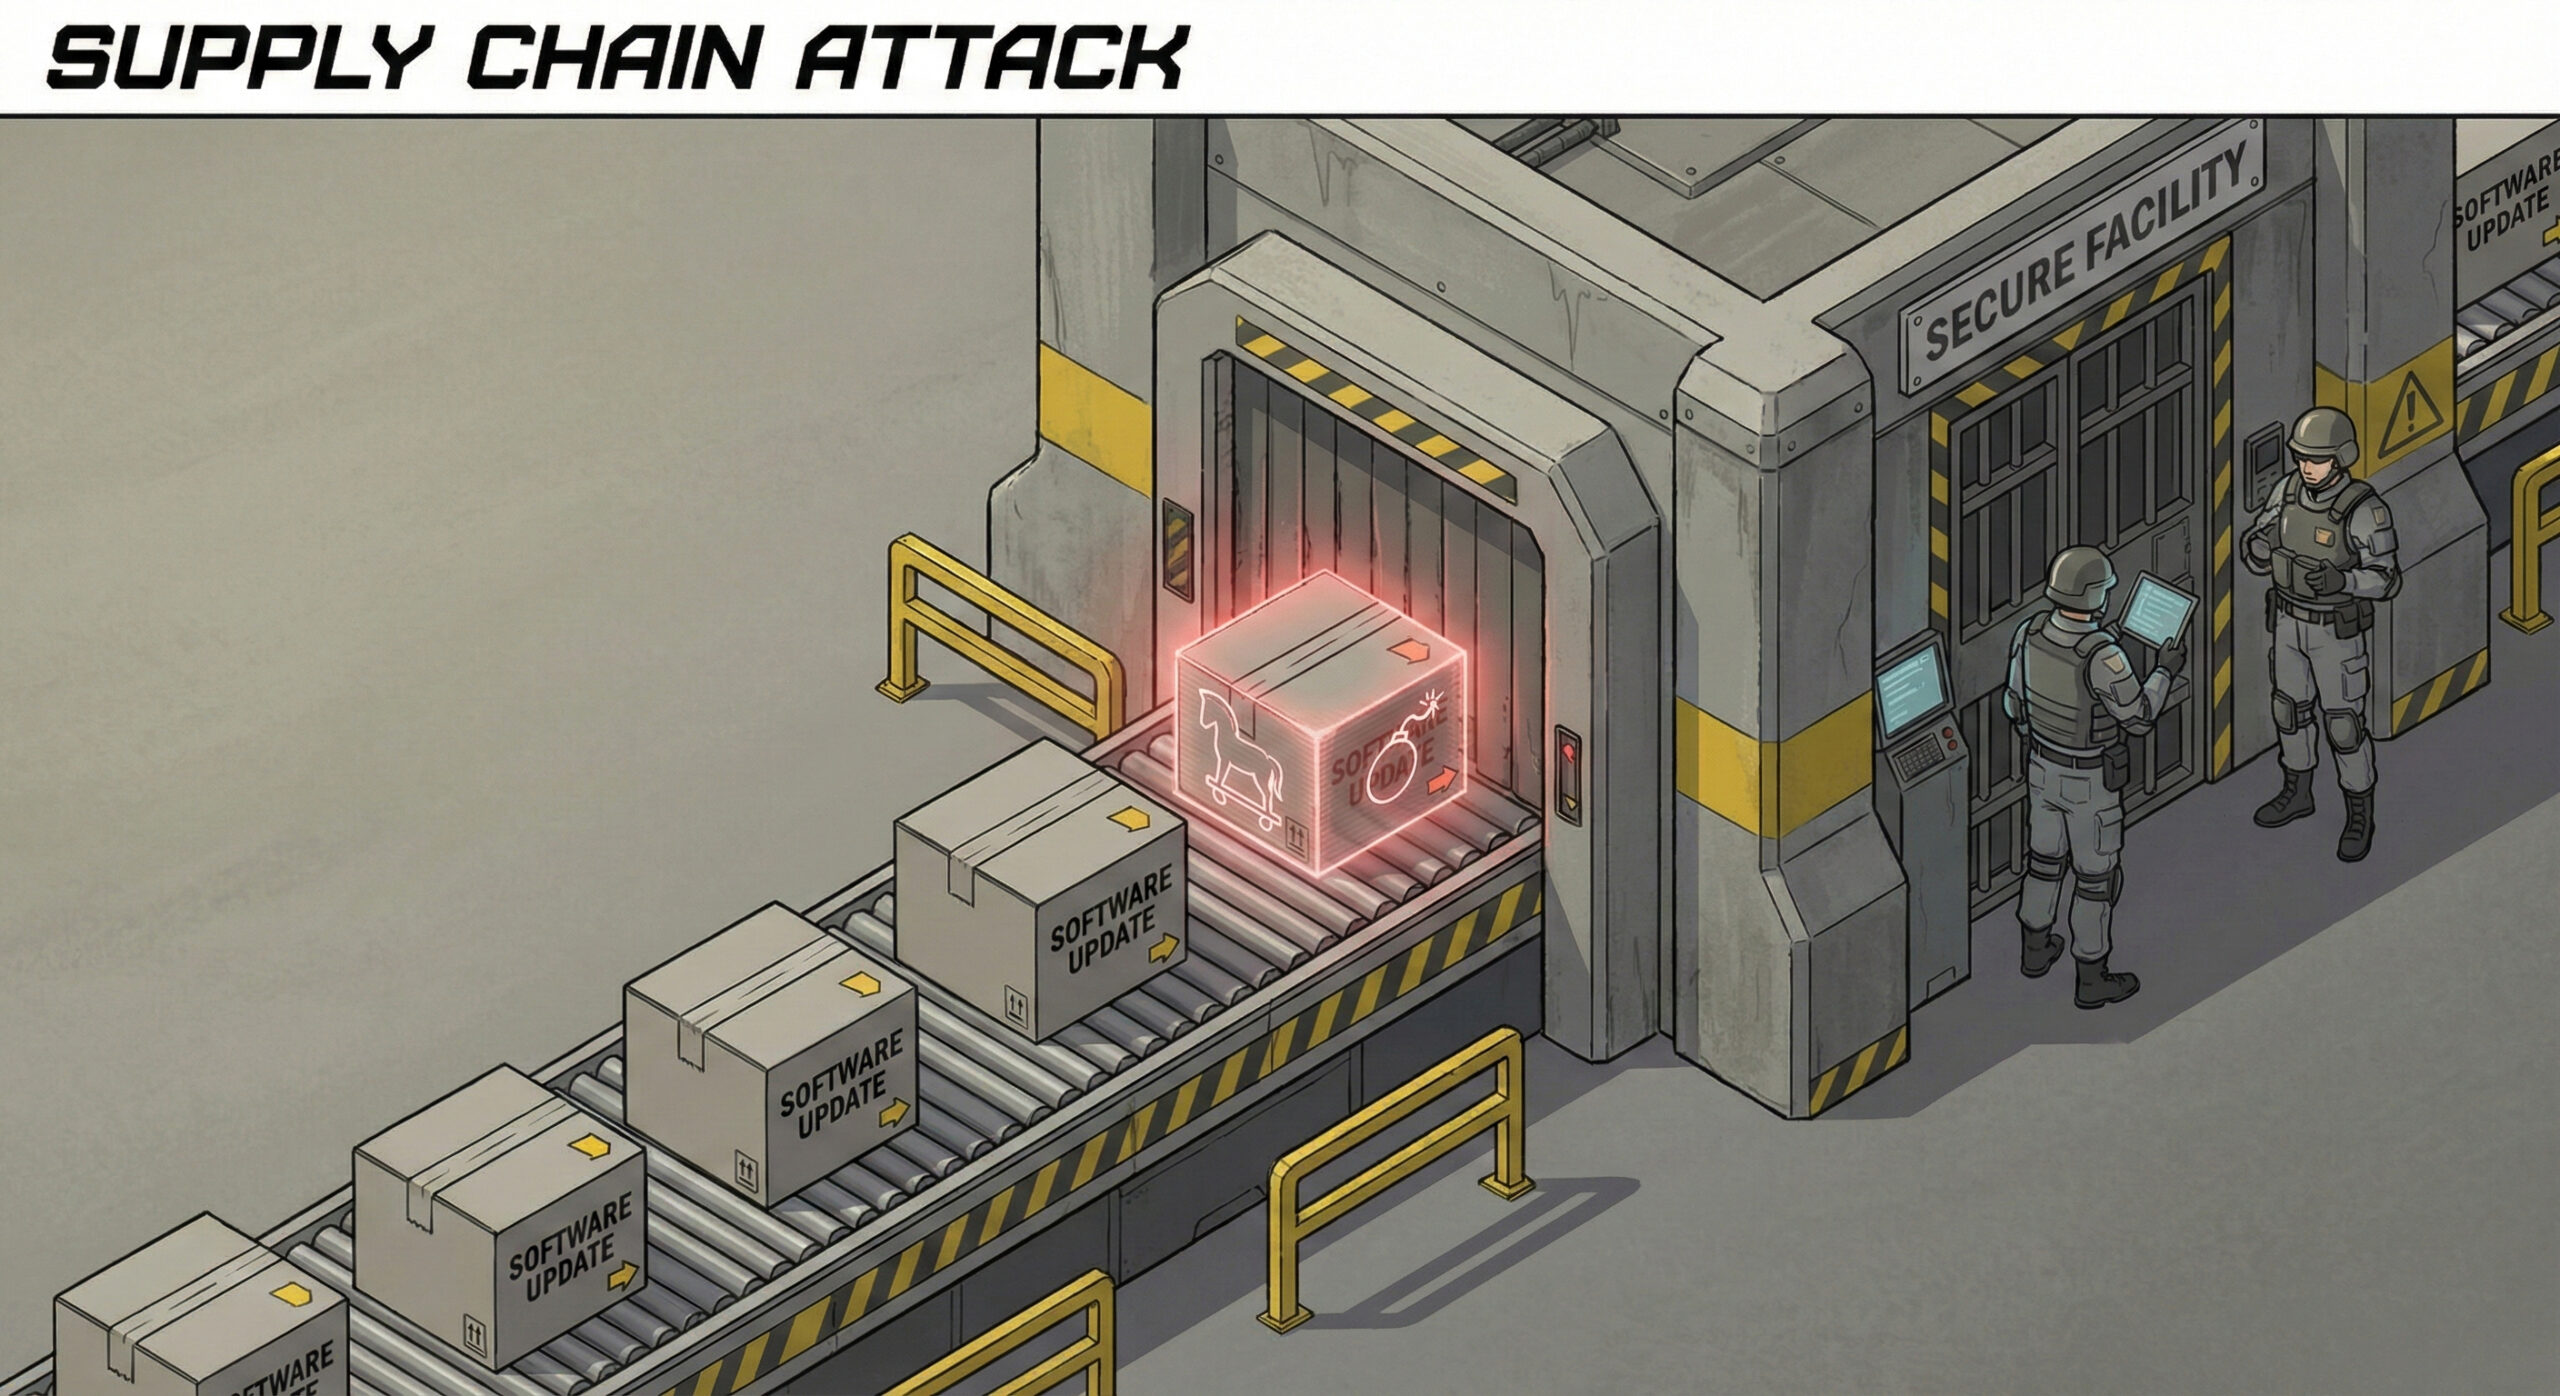
Imagine you have installed the most expensive armoured door at your company's entrance, and you have CCTV cameras and guards. Nobody can get in uninvited. But what do you do if the thief is the very plumber you called to fix the sink, and whom you let in of your own free will?
In the digital world, this scenario is called a Supply Chain Attack. In 2026, hackers have realised that big companies are hard to breach directly, so they attack easier targets: their software suppliers. At Altanet Craiova we consider this one of the most insidious risks for today's business environment.
What does a supply chain attack mean?
Modern companies do not build all their software from scratch. We use dozens of "ready-made" programs: accounting applications, website plugins, printer drivers or network monitoring platforms.
Hackers don't attack you. They breach the servers of the company that produces that software (the supplier) and infect the next update. You, being a conscientious customer, run the update believing it is for your own good. In reality, you have just installed the virus yourself, right into the heart of your system.
Why is it so dangerous?
This type of attack bypasses almost all classic security measures:
- Blind trust: Your antivirus trusts software digitally signed by major vendors (such as Microsoft, Adobe or local ERP providers). If the source is compromised, the antivirus will not detect anything suspicious at first.
- Privileged access: Maintenance or administration programs usually run with maximum rights (Administrator). Once infected, they hand hackers the keys to the kingdom.
How do you protect yourself from your own suppliers?
It is difficult, but not impossible. You need to adopt a "Zero Trust" mindset (Trust no one):
- Software inventory: You must know exactly which programs run in your company and who makes them. Are you using an obscure WordPress plugin made by a student? That is a weak point.
- Behaviour monitoring: Even if a program is "trusted", if it suddenly starts sending data to a server in Russia or China in the middle of the night, it must be blocked immediately. EDR (Endpoint Detection and Response) tools do exactly that.
- Network segmentation: Don't let the print server communicate with the database server. If the printer supplier is compromised, the hackers should stay isolated there.
To see concrete examples and understand the mechanics behind these incidents, you can read the explanations in the Cloudflare Learning Centre on Supply Chain attacks.
Conclusion
Your security is only as strong as the weakest link in your supplier chain. It is not enough to guard yourself; you must demand high standards from everyone you work with.
Want to know whether your network is ready to detect suspicious activity coming from the inside? We offer advanced monitoring solutions and proactive IT services. Visit our contact page and let's secure the whole chain.
This material is part of the Altanet educational series on digital safety. Want to know what other risks you are exposed to this year? See the Complete list of cyber threats in 2026.