
We live in an interconnected world. Your online shop talks automatically to the bank for payments, to the courier for deliveries and to the invoicing software. Everything seems magical and fast. But have you ever wondered how these systems talk to each other?
They use digital "pipes" called APIs (Application Programming Interfaces). In 2026, API Vulnerabilities have become hackers' preferred route for stealing data in bulk, precisely because they are often left unmonitored. At Altanet Craiova we consider API security a top priority for any business that develops or uses modern software.
What Is an API and Why Is It an Easy Target?
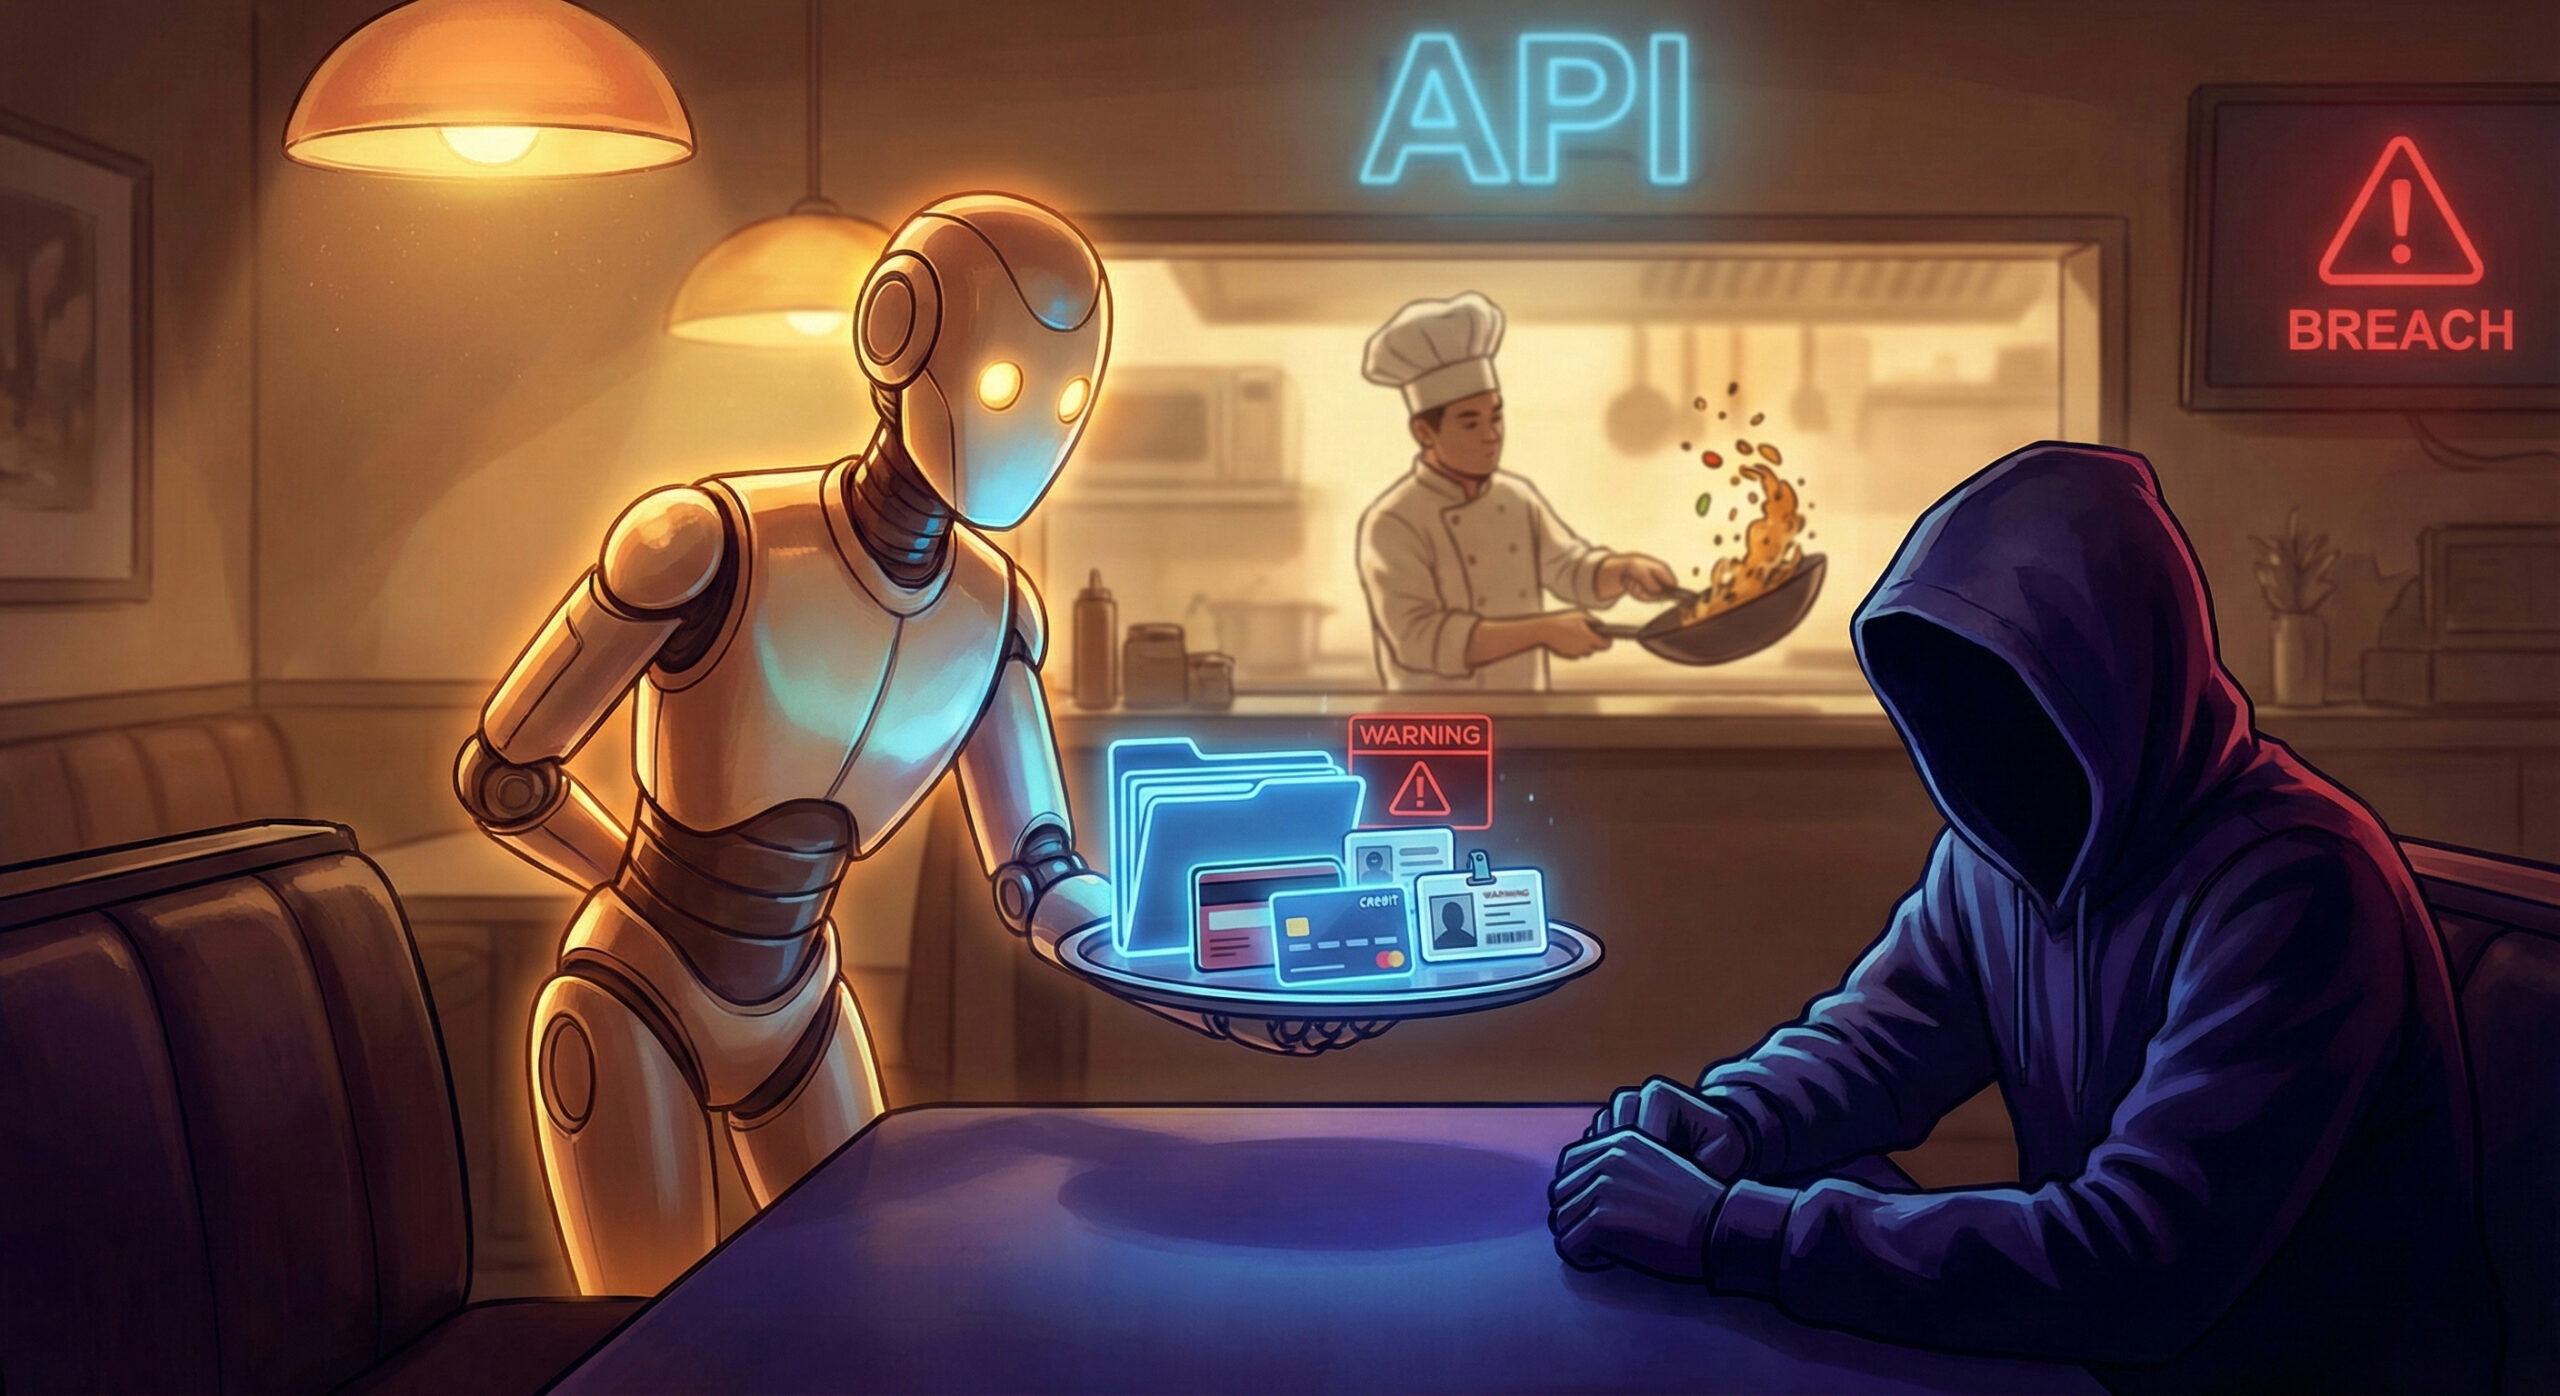
Think of an API as a waiter in a restaurant. You (the client/the app on your phone) sit at the table and ask the waiter (the API) for the menu or the food. The waiter goes to the kitchen (the server/database), takes what you asked for and brings it to you. You never enter the kitchen.
The problem appears when the "waiter" is not trained to check who is asking for the food. Vulnerabilities appear when hackers ask the waiter for things they should not receive, and he obediently brings them.
Examples of API Attacks (BOLA)
The most common type of attack is called BOLA (Broken Object Level Authorization). Let's take a simple example:
- You are logged into the courier app and want to see the status of your order with ID 1001.
- The app sends an API request: "Show me the details of order 1001".
- The hacker intercepts the request and simply changes the number: "Show me the details of order 1002", then 1003, 1004 and so on.
- If the API is vulnerable, it does not check whether the hacker has the right to see order 1002, it just delivers it. This way, the attacker can download the entire database of addresses and names without cracking a single password.
How Do You Secure Your Digital "Doors"?
API security is not solved with a simple antivirus, but through strict programming rules and monitoring:
- Strict Authentication and Authorisation: It is not enough for the user to be logged in. The API must check on every request: "Does this user have the right to see EXACTLY this document?".
- Rate Limiting: If someone asks for details on 1000 orders in one minute, it is clearly an attack. The system must automatically block these excessive requests.
- Don't expose unnecessary data: Sometimes the API sends the user's phone the customer's entire file (personal ID number, address, history), even though the app only displays the name. Hackers can see this hidden data in the traffic. Send only what is strictly necessary.
This topic is so critical that the global organisation OWASP has a top list dedicated exclusively to these risks. You can study the OWASP API Security Top 10 for technical details.
Conclusion
APIs are the engine of digital transformation, but they can also be its Achilles' heel. Don't leave windows open to your database. Test your applications before hackers do.
Do you have a mobile app or an online shop and want a penetration test for your API? Our team offers security audits and specialised IT services . Visit our contact page and make sure your data stays private.
This material is part of the Altanet educational series on digital safety. Want to know what other risks you are exposed to this year? See The Complete List of Cyber Threats in 2026.