
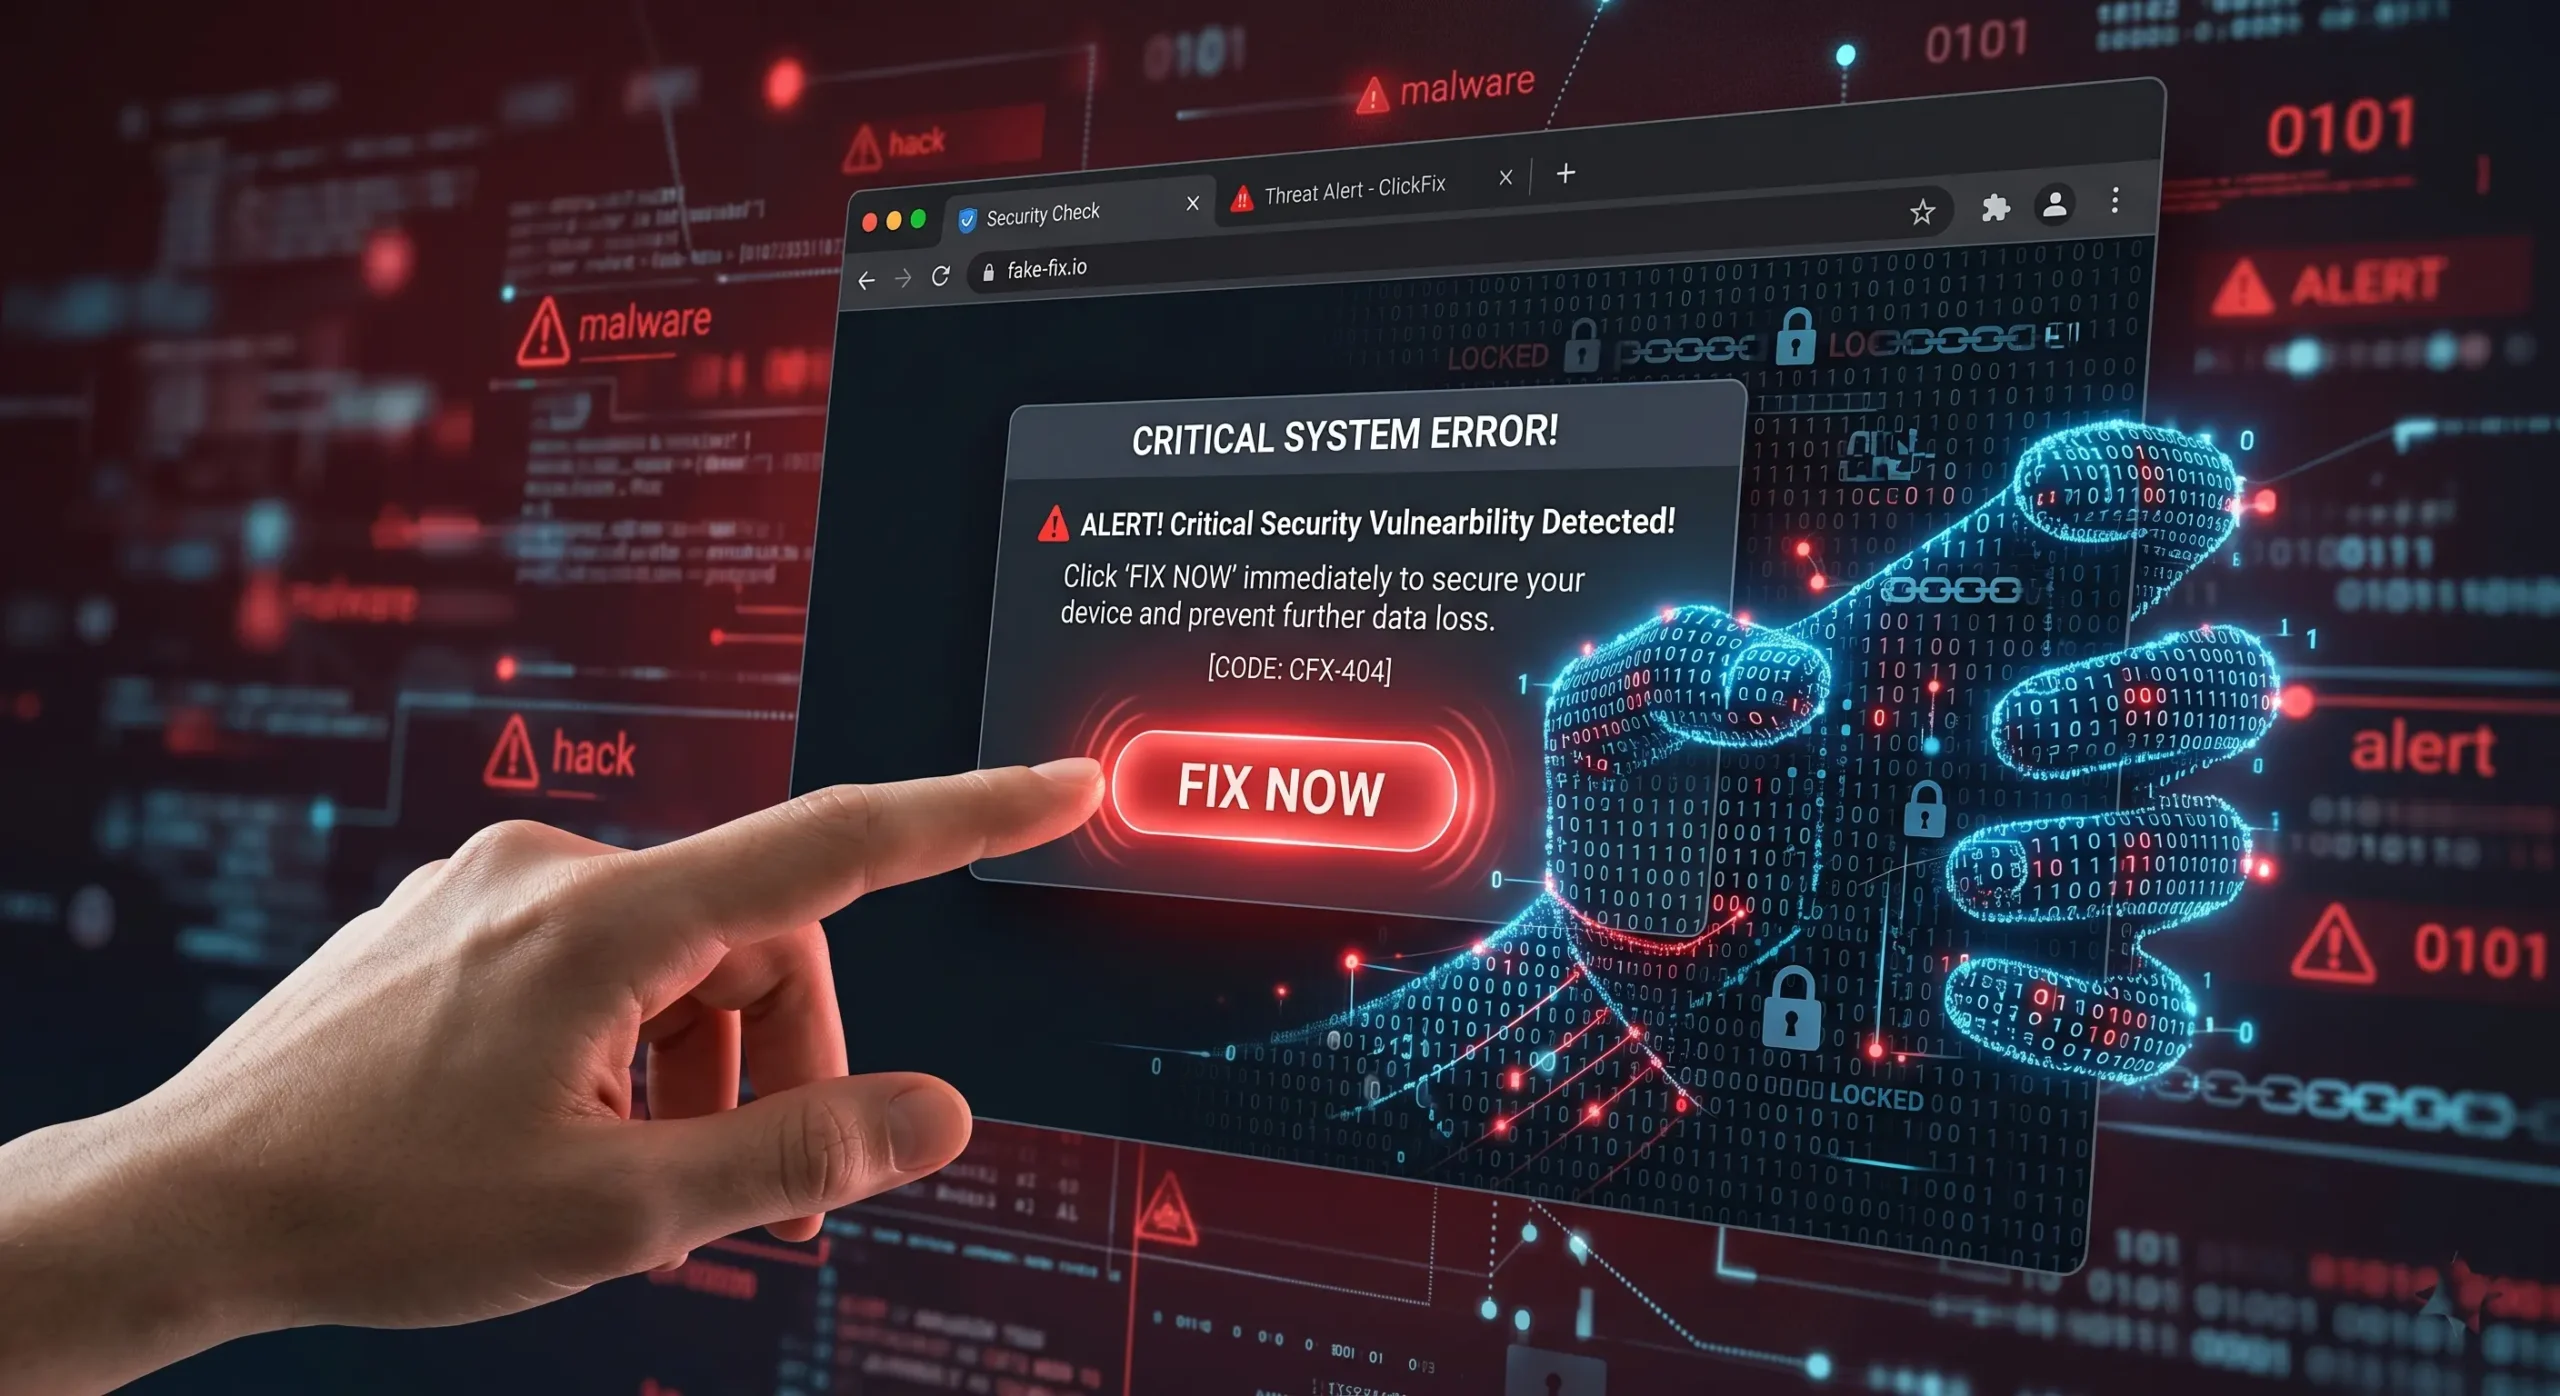
In 2026, cyberattacks have become extremely ingenious. A new method called "ClickFix" is wreaking havoc among internet users. This technique does not use suspicious email attachments. It relies on fake error messages that appear directly in your browser. At Altanet Craiova we have observed that this method is very effective. It fools even users who are alert to classic phishing emails.
According to the Proofpoint threat report, ClickFix uses social engineering at a higher level. Attackers create web pages that perfectly imitate system or software errors. The message tells you that your browser has a technical problem. Then you are offered a quick fix: press a "Fix" button or run a simple command in the terminal.
How does the ClickFix trap work in 2026?
It all starts on a seemingly harmless site. It could be a news page or a discussion forum. When you open the page, a pop-up window appears that imitates the Windows or Google Chrome interface. The message tells you that the browser cannot display the content correctly. You are asked to copy a small piece of code and run it in PowerShell to fix the error.
Many employees believe they are carrying out a legitimate repair. In reality, that code downloads and installs dangerous malware in the background. Within a second, the attackers take total control of your computer. They can steal passwords and confidential documents, or lock the system for ransom. ClickFix is dangerous because it does not require downloading a traditional file.
Signs that help you identify a ClickFix attack
There are a few details that give away this sophisticated attack method:
- Unexpected error messages: Your browser will never ask you to run code in PowerShell to view a website.
- Repair buttons on dubious sites: If an unknown site offers you unsolicited "technical help", it is almost certainly a scam.
- Copy-Paste instructions: Be extremely suspicious if you are asked to copy text and run it in the command line.
- The look of the pop-up window: Even if it imitates Windows, there may be small font mistakes or slightly altered logos.
How can you defend yourself against a single fatal click?
To stop ClickFix attacks, Altanet Craiova recommends strict digital discipline. Here are the rules you should follow:
- Training employees: The whole team must know that websites do not offer legitimate system repairs through pop-up windows.
- Blocking automated scripts: Implement solutions that prevent users without administrator rights from running code in the terminal.
- Keeping the browser constantly updated: New versions of Chrome or Edge already have filters that are beginning to identify these tactics.
Conclusion
In 2026, a single wrong click can stop an entire business. ClickFix shows how easily the human eye can be fooled by a familiar interface. Real protection comes from education and from using smart security tools. Be sceptical of any quick "fix" that appears out of nowhere on the internet.
This article is part of the Altanet series on cyber threats in 2026. Next article: NIS2 and DORA: A practical guide to complying with the new European laws. See also the complete guide to the series.