
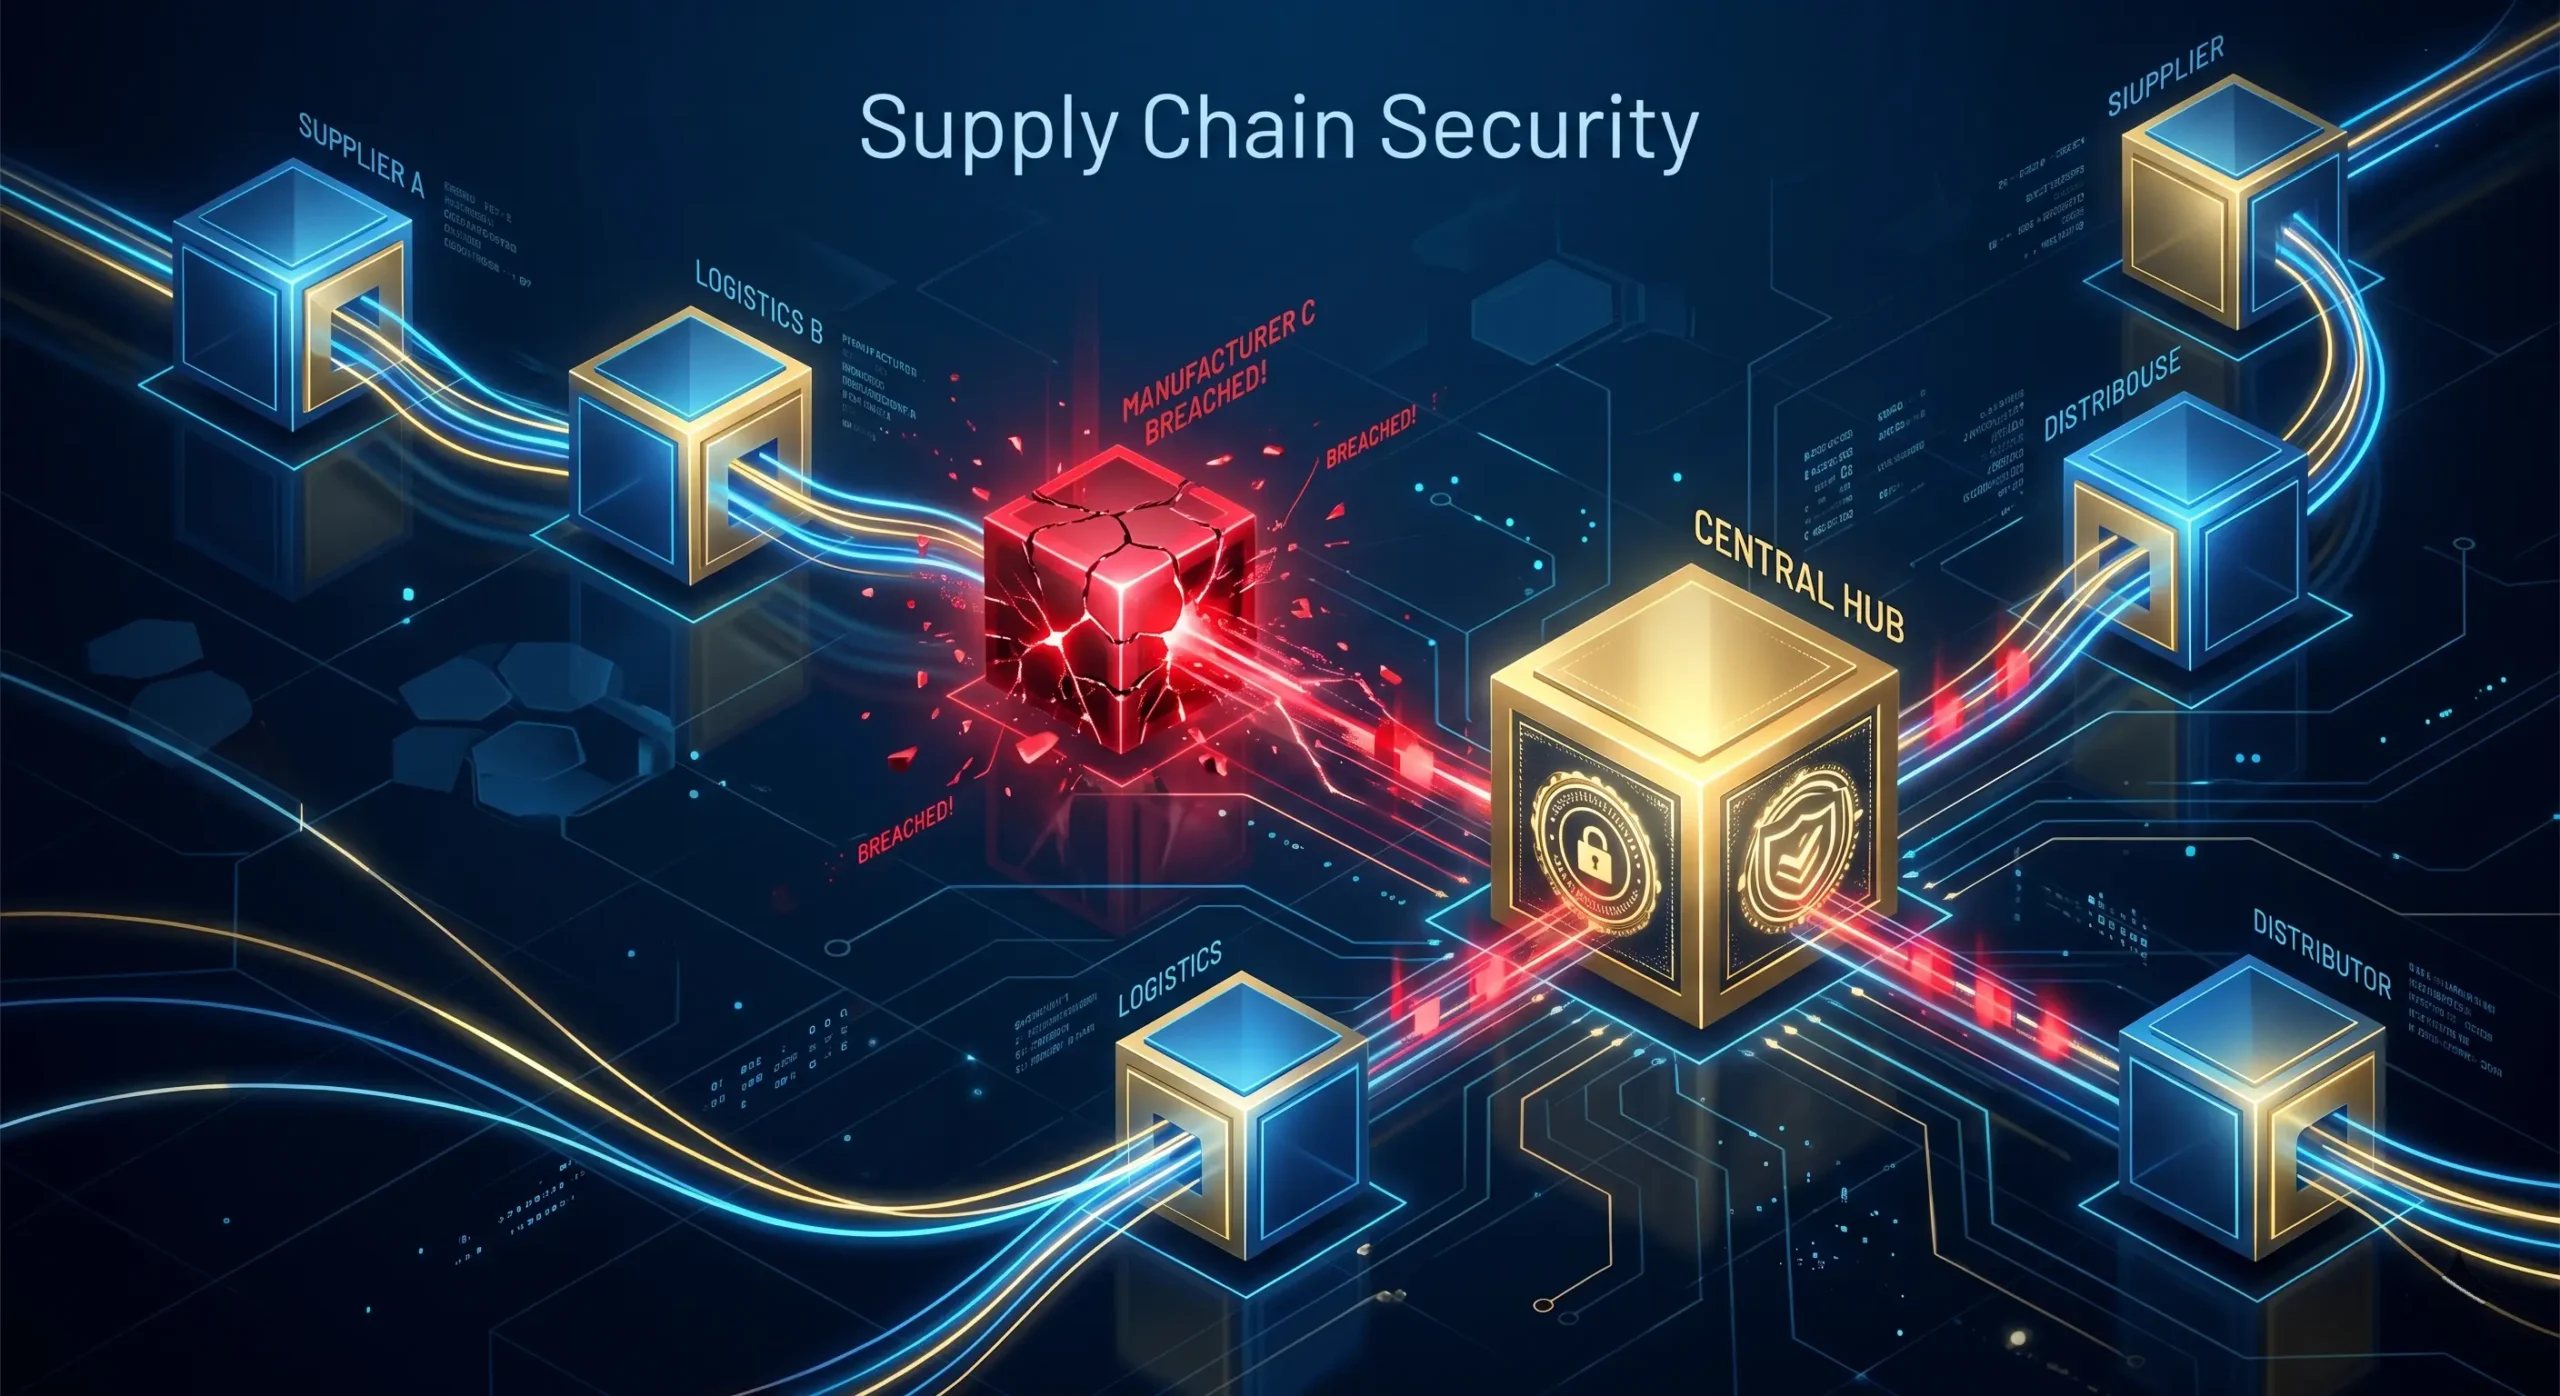
In 2026, you can have the best defence systems in the world and still fall victim to a cyberattack because of a business partner. Supply chain attacks have become hackers' preferred method of getting into large companies through the "back door". At Altanet Craiova we have noticed that small and medium-sized companies offering IT or maintenance services are often used as launch pads for much broader attacks.
According to Sangfor analyses, third-party vulnerabilities are now one of the biggest security challenges. Attackers don't target you directly, but compromise a trusted supplier to reach your data.
What does a supply chain attack mean?
This type of attack involves compromising a supplier of products or services in order to infect its customers. In 2026, this most often happens through infected software updates or through access to your partners' technical support accounts.
Imagine the company that manages your accounting software or server maintenance suffers a breach. Hackers use that company's legitimate access to get into your network. Because the connection comes from a "trusted partner", your defence systems might not detect the intrusion immediately. It is the digital equivalent of a Trojan horse.
Why are these attacks so dangerous in 2026?
Modern supply chains are complex and interconnected. Here are the main reasons for concern:
- Implicit trust: We often grant administration rights to IT suppliers without monitoring what they do in our network.
- The domino effect: A single compromised supplier can lead to the infection of hundreds of customer companies at the same time.
- Access to sensitive data: Cloud or logistics service providers often have direct access to your databases.
- Bypassing classic barriers: The attack doesn't come from outside, but through communication channels that are already approved and considered safe.
How can you secure your business partnerships?
To reduce the risk, Altanet Craiova recommends a "Zero Trust" strategy in your relationship with third parties:
- Auditing suppliers: Before signing a contract, ask your partners what cybersecurity measures they apply.
- Limited access: Give partners access only to the network segments strictly necessary, and only for the duration of the intervention.
- Monitoring third-party accounts: Watch any activity coming from external support or maintenance accounts.
- Security clauses in contracts: Include the supplier's obligation to notify you immediately if it has suffered a breach.
Conclusion
Your safety is no longer an individual effort, but a collective one. In 2026, you are only as protected as your most vulnerable supplier. Careful partner selection and constant monitoring are the only ways to avoid a digital disaster coming through intermediaries.
Want to make sure your relationship with your suppliers does not put your data at risk? Altanet Craiova helps you assess the risks and secure third-party access in your company. Let's talk on the contact page about protecting your business.
This article is part of the Altanet series on cyber threats in 2026. Next article: Advanced phishing: how AI has made email traps impossible to detect. See also the complete guide to the series.